Finding a lost C2PA manifest with a TrustMark watermark
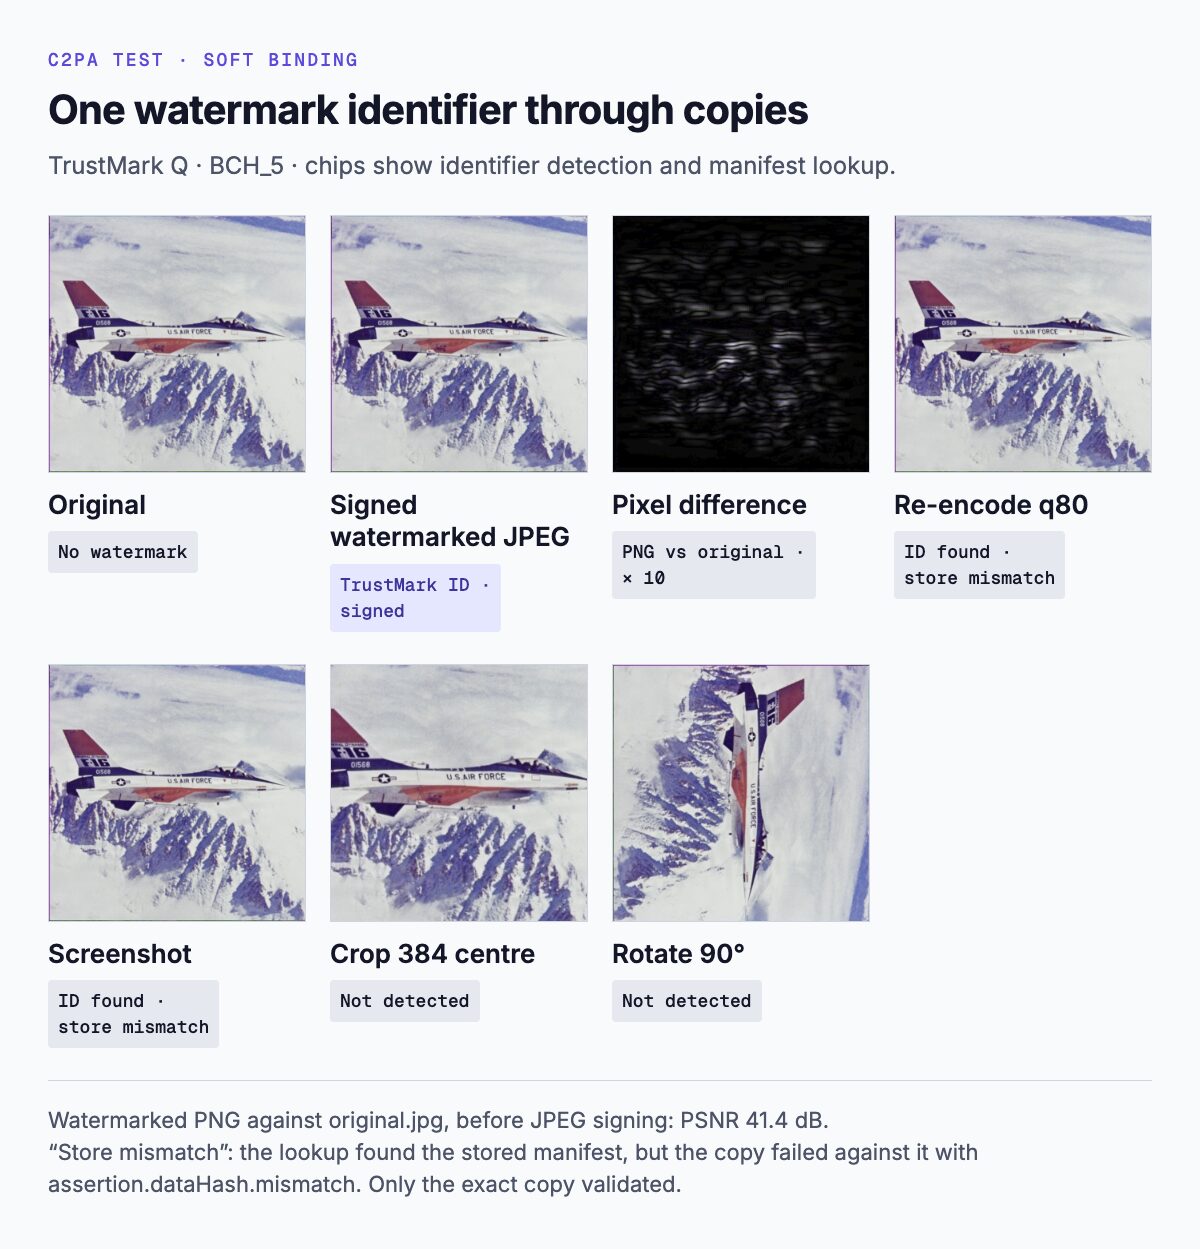
Our JPEG exports lost their embedded C2PA manifest, the signed provenance record stored inside the image file. We repeated the test with a TrustMark watermark carrying an identifier in the aeroplane’s pixels. After a quality-80 export, the manifest was gone but the identifier still led to our saved record. Reading that record against the exported file then returned assertion.dataHash.mismatch.
TL;DR
- The identifier survived re-encoding, resizing, PNG conversion, a screenshot, stripping, a byte edit and a comment, with 0 bit errors after correction.
- The centre crop and rotation gave no detection with
ROTATION=False. - Only the exact copy passed the recovered manifest’s file check; signing the re-encode with the recovered parent produced a new
Trustedrecord under our root. - Six unwatermarked images gave no detection; published TrustMark results distinguish a detected codeword from a match to a particular identifier.
The signing setup and the export results are covered in Where a signed JPEG loses its C2PA manifest.
A lookup that can survive changed bytes
C2PA’s Technical Specification describes a soft binding as an identifier, such as a fingerprint or invisible watermark, that can connect changed content to a manifest. It exists for cases where the bytes have changed or the embedded record has disappeared. The specification explicitly forbids using it as a hard binding, the cryptographic check against the asset’s bytes.
Our watermark identifier was a random value embedded in the image pixels, used as the key for a stored manifest. We used Adobe’s TrustMark to embed and decode it. We used the decoded value for a repository lookup to find the saved record under that identifier. Our repository was a local folder with an index mapping the identifier to a file.
C2PA’s Soft Binding Resolution API separates queries from manifest fetching. Our folder stood in for that repository step; it did not implement the API. In the experiment, decoding the identifier, finding the indexed file and validating the retrieved record were separate operations.
Embedding the identifier, then signing
We embedded the identifier in the aeroplane image, saved the watermarked pixels as a lossless PNG, then exported that to wm.jpg at sips quality 95. We signed the JPEG as signed-wm.jpg and extracted its manifest store, the packaged signed record, into the indexed local folder.
| Item | Setup |
|---|---|
| Watermark | TrustMark 0.9.2, variant Q, BCH_5; 61-bit random identifier, default strength |
| Execution | CPU inference on Ubuntu 24.04; Python 3.12.3; torch 2.11.0+cu128 |
| Tools | c2patool 0.26.30, sips-316, OpenSSL 4.0.3 |
| Image difference | Watermarked PNG against original.jpg: PSNR 41.43 dB |
| Signing | Local P-256 root and leaf; ES256; no trusted timestamp |
| Reads | Our test root; remote-manifest and online certificate-status fetching disabled |
| Record | c2pa.created, c2pa.watermarked.bound and c2pa.soft-binding |
BCH_5 names the error-correction setting used for the identifier. PSNR is a numerical comparison of image pixels; the reported value applies to the watermarked PNG against the original JPEG’s decoded pixels, before the quality-95 JPEG export. It is not a measurement of whether a person noticed the watermark.
The saved assertion, a statement inside the manifest, recorded com.adobe.trustmark.Q as its algorithm. These selected lines preserve the stored value, which followed the TrustMark example’s schema*identifier format:
        "alg": "com.adobe.trustmark.Q",
...
            "scope": {},
            "value": "1*0010000001110100111110010110000101100110101001100101110011111"
We indexed the extracted store by the identifier. Detection returned the lookup key; the manifest itself came from the folder, rather than from the decoded watermark.
Ten copies: finding the record and checking it
We made ten copies from signed-wm.jpg, decoded each with ROTATION=False, and used any recovered identifier to look up the stored manifest. We then checked each retrieved manifest against the copy with our test root. Bit errors in the table compare the decoded identifier with our expected value after error correction.
| Copy | Embedded manifest | TrustMark ID | Repository | Recovered validation |
|---|---|---|---|---|
| Exact copy | Yes | Detected, 0 bit errors | Found | Trusted; assertion.dataHash.match |
| Re-encode q80 | No | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| Resize 256 | No | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| PNG conversion | No | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| Screenshot | No | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| C2PA segments stripped | No | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| One byte changed | Yes | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| Comment segment added | Yes | Detected, 0 bit errors | Found | Invalid; assertion.dataHash.mismatch |
| Crop 384 centre | No | Not detected | Not found | Not attempted |
| Rotate 90° | No | Not detected | Not found | Not attempted |
For the screenshot, we displayed the signed watermarked JPEG at 512 × 512 and used Chromium’s capture function. The 384 × 384 centre crop was saved at quality 80.
Finding the record did not make the changed copies pass its file check. Only the exact copy returned Trusted against the recovered store. Even stripping just the C2PA segments failed: that copy was byte-identical to unsigned wm.jpg, but the recovered record had been extracted from the embedded layout in signed-wm.jpg.
We used a separate control with the unwatermarked JPEG to examine this layout effect. A sidecar is a manifest kept in a separate file. We compared a store extracted from signed.jpg with a sidecar independently signed over original.jpg. The independently signed output image stayed byte-identical to original.jpg and contained no embedded C2PA segments.
| Record supplied | Image checked | Default | Test root |
|---|---|---|---|
| Extracted store | signed.jpg | Valid | Trusted |
| Extracted store | Stripped copy | Invalid | Invalid |
| Extracted store | Re-encode q80 | Invalid | Invalid |
| Independent sidecar | Stripped copy | Valid | Trusted |
| Independent sidecar | Re-encode q80 | Invalid | Invalid |
Every Invalid row here reported assertion.dataHash.mismatch. The extracted store retained an exclusion range starting at byte 20 and covering 136,195 bytes, the original embedded C2PA region. An exclusion range tells the hash calculation which positions to skip; the Technical Specification describes hashing the asset outside those declared ranges.
After stripping, the file no longer had that region, but the extracted store still specified the same positions. Recomputing its hash reproduced the stored value for signed.jpg and a different value for the stripped file. The independent sidecar had no exclusion ranges and validated the stripped file, which exactly matched the unsigned original. The recovered watermarked record likewise retained its own embedded file’s exclusion range; recovery found that record without rewriting its binding.
Signing a new file with the recovered parent
We signed the quality-80 re-encode as a new asset, supplying the recovered manifest as its parent. An ingredient is C2PA’s record of an input asset; here it carried the recovered parent. The derivative’s new active manifest recorded c2pa.opened and c2pa.transcoded actions.
| Check | Result |
|---|---|
| Parent record | ingredient.manifest.validated |
| Derivative file | assertion.dataHash.match |
| Default trust | Invalid; signingCredential.untrusted |
| Test root | Trusted |
| Against original store | Invalid; assertion.dataHash.mismatch |
Against its own new manifest, the derivative passed; against the original stored manifest, it still failed the data-hash check.
C2PA’s Implementation Guidance describes this case: a transformed asset gets a new manifest with recovered provenance as an ingredient and a record that it was disconnected and retrieved.
Six images without a watermark
We also ran the detector on six unwatermarked images with the same decoder setting. The TIFF-derived inputs were PNG files prepared from those sources.
| Input | Detection |
|---|---|
| Original JPEG | Not detected |
| Signed, never watermarked JPEG | Not detected |
| Aeroplane TIFF source, as PNG | Not detected |
| Greyscale aeroplane | Not detected |
| Greyscale boat | Not detected |
| Boat TIFF source, as PNG | Not detected |
None returned a detection. Six images is a small check, and it doesn’t establish a false-match rate.
Kazempourradi et al. report that four TrustMark variants returned a valid codeword on at least one of four blind decodes for 5.9–15.3% of unmarked images. A codeword here is a decoded value accepted by the watermark’s coding checks. Their separate expected-payload comparison required 74 of 100 bits to match and produced no own-payload false match on the 85 tested images. Detecting an accepted value and matching a particular expected identifier are different measurements.
C2PA’s Security Considerations describes soft-binding collisions and repository injection that attach misleading provenance to content while leaving the substituted record’s signature intact. A collision is a wrong match between content and a binding; repository injection supplies a misleading record through the repository.
None of our six unwatermarked inputs got as far as a lookup.
References
- C2PA, “Content Credentials: C2PA Technical Specification,” version 2.5, October 2026.
- C2PA, “Soft Binding Resolution API,” version 2.5.
- C2PA, “Implementation Guidance,” version 2.2, §4.2.4.
- C2PA, “Security Considerations,” version 2.4, §§2 and 4.
- Adobe, “TrustMark,” repository README and C2PA example.
- Seyedmahdi Kazempourradi, Ramtin Mojtahedi and Behrang Mohseni, “Watermarks and Fingerprints as Soft Bindings for Content Provenance: An Open-Licence Benchmark for Images, Audio and Video,” arXiv preprint, 2 October 2026.